Identity & Access Management
NABCO provides Identity & Access Management (IAM) solutions that help organizations secure user identities, control access to critical systems, and reduce the risks associated with unauthorized access.
Identity & Access Management That Strengthens Your Security
Modern organizations rely on multiple applications, cloud platforms, networks, and business systems. Without proper identity controls, compromised credentials or excessive permissions can expose sensitive information and critical resources.
NABCO helps businesses establish a structured identity and access framework that ensures users receive the right access to the right resources at the right time.
Our IAM solutions support stronger security, simplified user management, improved compliance, and better visibility across your digital environment.
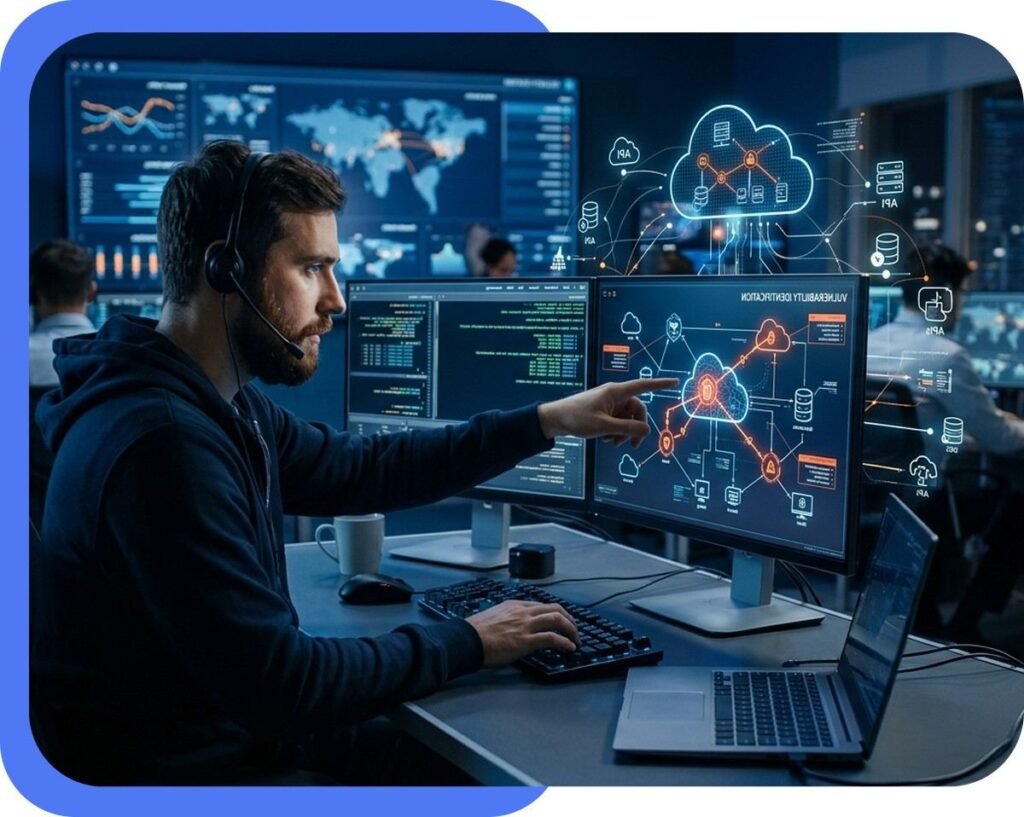
Penetration Testing Services
Network Penetration Testing
Assess internal and external network infrastructure to identify vulnerabilities, misconfigurations, exposed services, and potential attack paths.
Web Application Penetration Testing
Evaluate web applications for common and advanced security weaknesses affecting authentication, authorization, sessions, input validation, and sensitive data.
API Penetration Testing
Assess APIs for authentication, authorization, access-control, data exposure, and other vulnerabilities that could compromise connected systems.
Cloud Security Testing
Evaluate cloud environments and configurations to identify security weaknesses, excessive permissions, exposed resources, and potential attack paths.
Mobile Application Testing
Assess Android and iOS applications for vulnerabilities involving authentication, data storage, communications, APIs, and application logic.
External & Internal Infrastructure Testing
Simulate attacks against internet-facing assets to identify vulnerabilities that could be exploited from outside the organization.
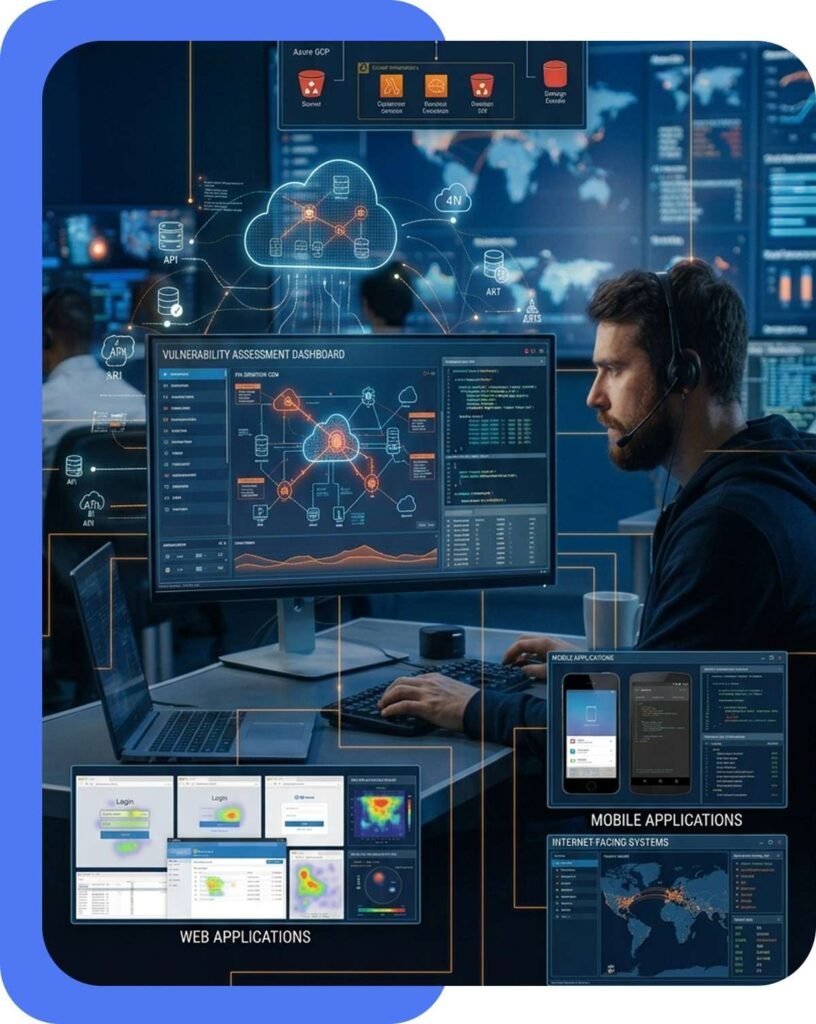
What We Test
- Network infrastructure
- Web applications
- APIs and web services
- Cloud environments
- Mobile applications
- Servers and endpoints
- Authentication systems
- Access controls
- Security configurations
- Wireless networks
- Internet-facing systems
- Critical business applications
Our Penetration Testing Approach
-
Reconnaissance & Discovery
We identify assets, services, technologies, and potential attack surfaces relevant to the assessment.
-
Vulnerability Identification
Our testing helps uncover weaknesses in systems, applications, configurations, authentication mechanisms, and security controls.
-
Controlled Exploitation
Where appropriate, identified vulnerabilities are safely validated to determine their actual security impact.
-
Risk Assessment
Findings are evaluated based on their severity, business impact, and potential exploitation risk.
-
Detailed Reporting
We provide clear findings, evidence, risk ratings, and practical recommendations for remediation.
-
Retesting & Validation
After remediation, vulnerabilities can be retested to verify that the required security improvements have been implemented effectively.
Why Choose NABCO for Penetration Testing?
Real-World Attack Simulation
Testing is designed to replicate realistic attack techniques and identify vulnerabilities that could affect your business.
Business-Focused Security
We translate technical vulnerabilities into clear business risks, helping decision-makers prioritize remediation.
Comprehensive Assessment
We assess multiple layers of your technology environment to provide a broader view of your security posture.
Actionable Recommendations
Our reports provide practical remediation guidance rather than simply listing vulnerabilities.
Security-Focused Methodology
Testing is performed in a controlled and structured manner to minimize operational disruption.
Support Beyond the Report
NABCO can assist with remediation guidance, security improvements, and follow-up validation.
Turn Vulnerabilities Into Security Improvements
Don’t wait for a cyberattack to reveal weaknesses in your environment. Proactive penetration testing can help your organization identify security gaps, reduce exposure, and make informed security decisions.
Frequently Asked Questions (FAQs)
Penetration testing is a controlled security assessment that simulates real-world cyberattacks to identify and validate vulnerabilities in systems, applications, networks, and infrastructure.
Penetration testing helps identify security weaknesses before attackers can exploit them. It can also support risk management, security improvement, and compliance requirements.
The appropriate frequency depends on your environment, risk profile, regulatory requirements, and frequency of major changes. Regular testing is recommended, particularly after significant infrastructure or application changes.
Testing is planned and controlled to minimize operational impact. Before testing begins, the scope, rules of engagement, and testing limitations are agreed upon.
NABCO provides detailed findings and practical remediation recommendations. Follow-up testing can also be performed to verify that identified vulnerabilities have been resolved.
Yes. Penetration testing can cover web applications, APIs, cloud environments, external infrastructure, internal networks, and other approved technology assets.