SOC Services
Protect your organization from evolving cyber threats with NABCO’s Security Operations Center (SOC) Services.
What Are SOC Services?
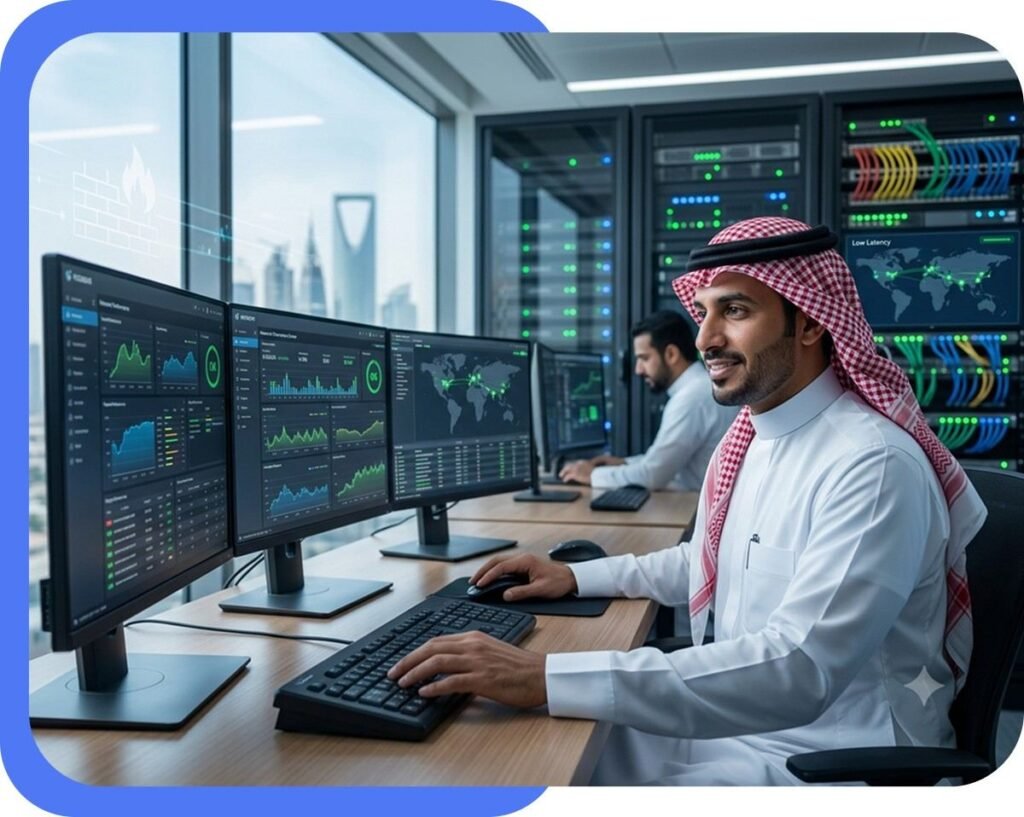
A Security Operations Center (SOC) is a centralized security function responsible for continuously monitoring and protecting an organization’s digital environment.
Our SOC services combine skilled cybersecurity professionals, advanced security technologies, threat intelligence, and structured response processes to identify and address potential security threats before they cause serious business disruption.
Our Cloud Security Services
24/7 Security Monitoring
Continuously monitor your IT infrastructure, networks, endpoints, servers, and security events to identify suspicious activities and potential threats.
Threat Detection & Alerting
Detect unusual behavior, unauthorized access attempts, malware activity, and other indicators of compromise through continuous security monitoring and analysis.
Security Incident Investigation
Analyze security alerts and investigate potential incidents to determine their severity, scope, and possible impact on your organization.
Incident Response Support
Support rapid containment and response to security incidents to help minimize disruption, reduce potential damage, and restore normal operations.
SIEM Monitoring & Management
Monitor and analyze security logs and events through Security Information and Event Management (SIEM) solutions for improved visibility and threat detection.
Log Management & Analysis
Collect, correlate, and analyze security logs from multiple systems and devices to identify suspicious patterns and potential security risks.
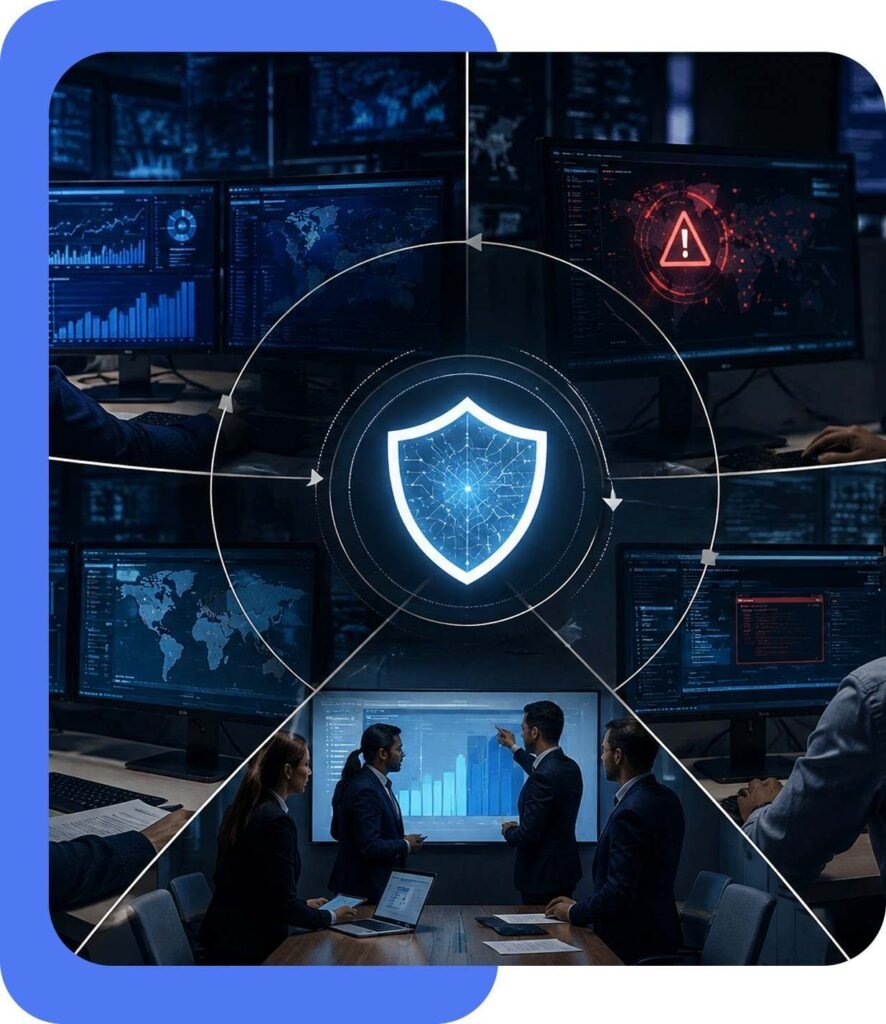
How Our SOC Works
Monitor
We continuously monitor security events and activities across your IT environment.
Detect
Potential threats and suspicious activities are identified using security tools, analytics, and expert analysis.
Investigate
Security alerts are analyzed to determine whether they represent genuine threats and assess their potential impact.
Respond
Appropriate response actions are initiated to help contain and address confirmed security incidents.
Benefits of SOC Services
- Continuous 24/7 security monitoring
- Improved threat visibility
- Faster detection of suspicious activities
- Rapid investigation of security alerts
- Reduced incident response time
Stay Ahead of Cyber Threats
Strengthen your organization’s cybersecurity with continuous monitoring, advanced threat detection, and expert security response.
Frequently Asked Questions (FAQs)
SOC Services provide continuous cybersecurity monitoring, threat detection, investigation, and incident response support to help organizations protect their IT infrastructure and digital assets.
Cyber threats can occur at any time. SOC Services provide continuous monitoring and expert security analysis to help identify and respond to potential threats before they cause significant business disruption.
SOC services are designed to provide continuous security monitoring and threat detection, helping organizations maintain visibility into potential threats around the clock.
A SOC can help identify suspicious activities such as unauthorized access attempts, malware, ransomware indicators, unusual network activity, compromised accounts, and other potential security incidents.