Leading Cybersecurity Companies in Saudi Arabia: 2027 Guide
Saudi Arabia has a large and increasingly specialized cybersecurity ecosystem. Businesses can choose from national-scale providers, licensed Managed Security Operations Center operators, specialist cybersecurity companies, enterprise technology integrators and technology providers that combine cybersecurity with broader IT infrastructure services.
The market is substantial. The National Cybersecurity Authority reported that cybersecurity spending in Saudi Arabia reached SAR 15.2 billion in 2024, 14% higher than in 2023, with private-sector organizations accounting for SAR 10.3 billion.
But choosing among cybersecurity companies in Saudi Arabia should not begin with a simple “top 10” ranking.
A 30-person company that needs Microsoft 365 security, endpoint protection, firewall management and IT support has very different requirements from a government entity or Critical National Infrastructure operator looking for a Tier 1 Managed Security Operations Center.
There is no single cybersecurity company that is best for every Saudi organization.
This guide compares selected cybersecurity providers operating in Saudi Arabia, explains where their capabilities differ and shows what businesses should check before creating a shortlist.
Verification note: Company capabilities and MSOC status in this guide are based on publicly available information reviewed in October 2026. Regulatory status, licences and service portfolios can change. Always verify current information with the provider and relevant NCA directory before procurement in 2027.
Cybersecurity Companies in Saudi Arabia at a Glance
The companies below are selected notable providers rather than a universal best-to-worst ranking or complete directory.
“Leading” in this guide means providers with publicly verifiable Saudi operations, cybersecurity capabilities or relevant market positioning. It does not mean an official NCA ranking or independent performance ranking.
| Company | May Be Suitable For | Key Cybersecurity Focus | MSOC Status / Regulatory Note |
|---|---|---|---|
| SITE | Government, regulated and large-enterprise environments | Sovereign cloud, MDR, SOC/NOC, cloud and network security | Tier 1 MSOC |
| sirar by stc | Enterprises needing broad cybersecurity capabilities | MDR, GRC, infrastructure, cloud, OT and incident response | Tier 1 MSOC |
| Cyberani | Industrial, enterprise and government organizations | Managed security, offensive security, OT, GRC and DFIR | Tier 1 MSOC |
| SAMI-AEC | Enterprise, government and sensitive environments | SOC, SIEM, monitoring, assessments and cyber solutions | Tier 1 MSOC |
| Innovative Solutions | Organizations seeking specialist consulting and managed security | Advisory, assurance, GRC and managed security | Tier 2 MSOC |
| Security Matterz | Organizations seeking managed and specialist cybersecurity | MDR, managed SOC, monitoring and advisory | Tier 2 MSOC |
| Sahara Net | Businesses combining ICT/network and managed security | SOC, SIEM, SOAR, monitoring and incident management | Tier 2 MSOC |
| Saudi Business Machines (SBM) | Larger organizations needing enterprise IT plus cybersecurity | Managed security, infrastructure security and incident response | Tier 2 MSOC |
| NABCO | SMEs and mid-market businesses needing cybersecurity integrated with IT infrastructure | Network, endpoint, Microsoft 365, cloud, identity, email, data and infrastructure security | Not presented here as Tier 1/2 MSOC; verify applicable NCA registration/licensing separately |
NCA’s current MSOC framework separately identifies Tier 1 and Tier 2 licensed providers. Tier 1 currently includes additional providers such as Haboob and Technology Control Company (TCC), so the table above should not be interpreted as the complete NCA-licensed-provider list. National Cybersecurity Authority
Publisher Disclosure
This guide is published by NABCO, and NABCO is included as one of the cybersecurity providers discussed.
NABCO’s inclusion is based on its publicly published cybersecurity service portfolio and Saudi operations. It is not presented as an NCA Tier 1 or Tier 2 MSOC operator unless such status can be independently verified through current official NCA sources.
Every provider in this guide should be independently evaluated against your organization’s requirements.
How We Selected the Companies in This Guide
This article does not claim to produce a mathematical ranking of the “best cybersecurity companies in Saudi Arabia.”
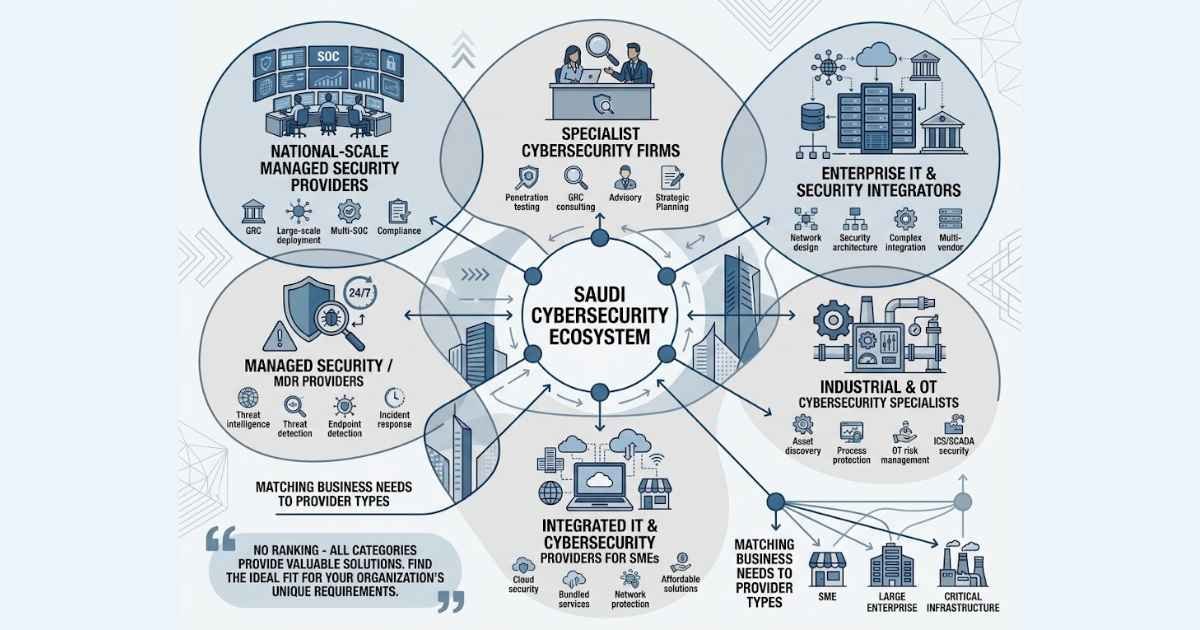
Instead, the selection represents different segments of the Saudi cybersecurity market, including:
- National-scale MSOC providers
- Specialist cybersecurity firms
- Enterprise IT and security integrators
- Managed-security providers
- Industrial and OT specialists
- Integrated IT and cybersecurity providers serving SMEs and mid-market businesses
Important considerations include Saudi presence, publicly verifiable cybersecurity capabilities, regulatory relevance, specialization, industry experience and whether sufficient information exists for buyers to evaluate the provider.
A large catalogue of cybersecurity services does not automatically make one company better than another.
The important question is whether the provider has strong, appropriate capabilities for the problem your organization needs to solve.
Selected Cybersecurity Companies in Saudi Arabia for 2027
SITE — Saudi Information Technology Company
May be suitable for: Government, highly regulated, large-enterprise and sovereignty-sensitive requirements.
SITE is a major Saudi technology and cybersecurity provider and appears among the NCA’s current Tier 1 MSOC providers.
Its published capabilities include areas such as:
- Managed Detection and Response
- SOC/NOC capabilities
- Cloud security
- DDoS protection
- Identity management
- Email security
- Network security
- SIEM/SOAR-related capabilities
- Backup and disaster recovery
SITE is particularly relevant where sovereign cloud, national-scale infrastructure and managed cybersecurity form part of the requirement.
Editorial assessment: Consider SITE where large-scale, regulated, government, CNI or sovereignty-sensitive technology requirements are central to the project.
sirar by stc
May be suitable for: Enterprises requiring broad cybersecurity, managed detection, GRC and infrastructure-security capabilities.
sirar by stc publishes cybersecurity capabilities covering areas such as:
- Managed Detection and Response
- DDoS protection
- GRC
- Cloud security
- OT security
- Endpoint security
- Infrastructure security
- Incident response
The NCA currently lists sirar by stc as a Tier 1 MSOC provider.
Its broad portfolio can be relevant to organizations requiring managed monitoring together with enterprise cybersecurity, governance, infrastructure and cloud-related services.
Cyberani
May be suitable for: Enterprises, industrial organizations and organizations requiring managed security combined with specialist capabilities.
Cyberani operates from Riyadh and Dhahran and publishes capabilities including:
- Managed security
- GRC
- Offensive cybersecurity
- Penetration testing
- OT cybersecurity
- Digital forensics
- Incident response
The NCA currently lists Cyberani among its Tier 1 MSOC providers.
Its OT and specialist-security capabilities may be particularly relevant to industrial organizations where cybersecurity extends beyond traditional office IT.
SAMI Advanced Electronics — SAMI-AEC
May be suitable for: Organizations requiring managed security operations and advanced enterprise cybersecurity.
SAMI-AEC publishes capabilities around:
- SOC services
- SIEM
- Continuous security monitoring
- Security assessments
- Threat detection
- Incident-response-related services
The company appears in the NCA’s current Tier 1 MSOC provider list.
Its wider technology background can make it relevant where cybersecurity forms part of a sensitive or large enterprise technology environment.
Innovative Solutions
May be suitable for: Businesses seeking specialist cybersecurity consulting, assurance, implementation and managed services.
Innovative Solutions has Saudi operations including Riyadh, Jeddah and Al Khobar.
Its published cybersecurity portfolio includes:
- Cybersecurity advisory
- GRC
- Managed security
- Technical assurance
- Vulnerability assessment
- Penetration testing
- Security implementation
- Cloud and infrastructure security
The NCA currently lists Innovative Solutions as a Tier 2 MSOC provider.
Its cybersecurity-focused model may suit organizations that need specialist security consulting as well as implementation and managed services.
Security Matterz
May be suitable for: Organizations seeking specialist managed cybersecurity and monitoring services.
Security Matterz is based in Riyadh and publishes services including:
- Managed Security Services
- Managed Detection and Response
- Managed SOC
- SIEM-related services
- Threat intelligence
- Vulnerability assessment
- Penetration testing
- Cybersecurity advisory
Security Matterz currently appears among the NCA’s Tier 2 MSOC providers.
Its focus may appeal to organizations that already have an internal IT capability but need a more specialized cybersecurity partner.
Sahara Net
May be suitable for: Businesses that want managed security alongside broader network, connectivity or ICT services.
Sahara Net operates across multiple Saudi locations and publishes managed cybersecurity capabilities including:
- SOC
- SIEM
- SOAR
- Security-event monitoring
- Incident management
- UEBA
- Intrusion detection
- Digital-forensics-related services
Sahara Net appears in the current Tier 2 MSOC list.
Its combination of telecommunications, networking, infrastructure and managed security may be useful for companies that want several related technology requirements handled together.
Saudi Business Machines — SBM
May be suitable for: Larger organizations seeking cybersecurity within an enterprise infrastructure and systems-integration environment.
SBM’s published security portfolio covers areas such as:
- Managed security
- Security intelligence
- Advanced threat protection
- Incident response
- Firewall and IPS
- Email and web security
- Vulnerability management
- Penetration testing
SBM currently appears in the NCA’s Tier 2 MSOC provider list.
Its enterprise technology background may be particularly relevant where cybersecurity is part of a wider infrastructure, systems-integration or managed-services project.
NABCO — Cybersecurity Services Integrated with Business IT
May be suitable for: SMEs and mid-market organizations that need cybersecurity implemented together with their everyday IT environment.
NABCO is a Saudi technology, IT and infrastructure solutions company with operations in Al Khobar, Jubail and Riyadh. Its wider service portfolio includes managed IT, cybersecurity, Microsoft and cloud solutions, networks, servers, backup and related technology infrastructure. NABCO Services
More importantly for this comparison, NABCO has a dedicated cybersecurity service portfolio rather than cybersecurity being mentioned only as a secondary IT capability.
Its Cybersecurity Solutions in Saudi Arabia page publishes services across the following areas:
- Network security
- Next-generation firewalls
- IDS/IPS
- Secure VPN
- Network Access Control
- Endpoint protection
- Security monitoring
- Identity and Access Management
- MFA and role-based access
- Vulnerability assessment
- Penetration testing
- Microsoft 365 and Azure security
- Cloud security
- Email and anti-phishing security
- Business Email Compromise protection
- Governance and compliance support
- Incident response
- Data recovery and disaster recovery
These services are currently listed directly on NABCO’s cybersecurity page. NABCO Cybersecurity Services
Where NABCO’s Position Is Different
NABCO should be recognized as a cybersecurity service provider, but it should not be positioned as though it serves exactly the same market requirement as a national-scale Tier 1 MSOC operator.
For many SMEs and mid-sized organizations, cybersecurity weaknesses are closely connected with everyday IT problems.
A business might simultaneously have:
- An outdated firewall
- Poorly segmented networks
- Unmanaged laptops
- Weak Microsoft 365 security
- Missing MFA
- Unsupported servers
- Inadequate backups
- Email-security weaknesses
- Limited internal IT resources
In this type of environment, the security problem cannot always be separated from the IT infrastructure.
An integrated provider can assess the weakness and then help implement changes across firewalls, networks, Microsoft 365, endpoints, servers, backups and related systems.
Editorial assessment: NABCO may be a suitable option for SMEs and mid-market organizations seeking practical cybersecurity improvements integrated with Microsoft technologies, networks, cloud, servers and ongoing IT infrastructure support.
NABCO Regulatory Disclosure
Cybersecurity-provider capability and regulatory status are separate matters.
This article does not describe NABCO as:
- NCA approved
- NCA certified
- Tier 1 MSOC licensed
- Tier 2 MSOC licensed
NCA states that entities providing cybersecurity services, solutions or products in Saudi Arabia fall within its provider registration and licensing framework, while MSOC services have a separate Tier 1/Tier 2 licensing framework. National Cybersecurity Authority
Any regulatory status relevant to a specific procurement should therefore be verified against the current official NCA information and NABCO’s legal entity details.
This distinction allows NABCO to be accurately identified as a cybersecurity service provider without making an unsupported regulatory or MSOC claim.
NCA Registration, Provider Licensing and MSOC Licensing
Saudi cybersecurity buyers should not treat these terms as interchangeable.
NCA Provider Registration
NCA states that registration is required for entities providing cybersecurity services, solutions or products in Saudi Arabia.
The registration requirement has applied since August 1, 2022. National Cybersecurity Authority
The official provider directory should be checked directly during procurement because company status may change.
Cybersecurity Services Provider Licensing
NCA also provides a broader Cybersecurity Services Providers Licensing service for organizations providing cybersecurity products, solutions or services in the Kingdom. National Cybersecurity Authority
This means Saudi provider regulation should not be simplified to only registration and MSOC licensing.
MSOC Licensing
Managed Security Operations Center services have a separate licensing structure.
Tier 1 MSOC permits service provision to all organizations, including government entities and organizations owning, operating or hosting Critical National Infrastructure.
Tier 2 MSOC excludes government and CNI entities.
Therefore:
Provider registration ≠ general provider licensing ≠ Tier 1 MSOC ≠ Tier 2 MSOC
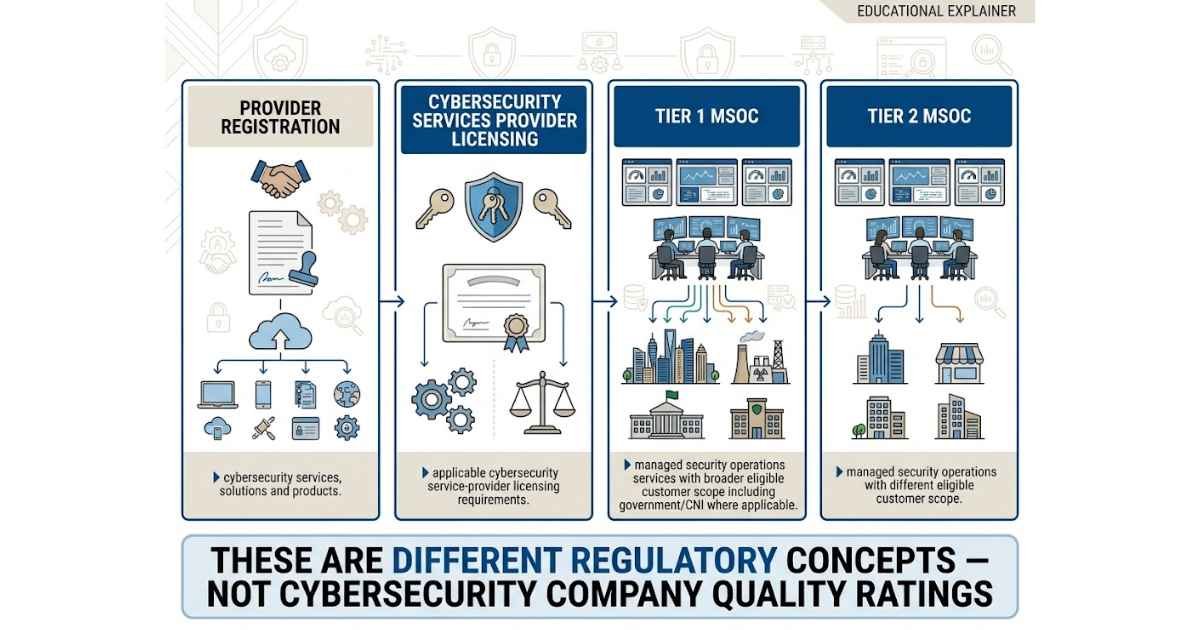
The appropriate requirement depends on the cybersecurity service being purchased.
What Cybersecurity Service Does Your Business Need?
Before comparing cybersecurity companies in Saudi Arabia, identify the problem first.
| Business Need | Service to Evaluate |
|---|---|
| Unsure where weaknesses are | Cybersecurity assessment |
| Network exposure | Firewall and network security |
| Employee-device risk | Endpoint protection / EDR |
| Microsoft 365 compromise | Identity and Microsoft 365 security |
| Sensitive business information | Data protection / DLP |
| Application weaknesses | Vulnerability assessment / penetration testing |
| Continuous threat monitoring | SOC / MDR / MSOC |
| Industrial systems | OT / ICS cybersecurity |
| Regulatory readiness | GRC / compliance consulting |
| Ransomware resilience | Endpoint + segmentation + backup / DR |
| Active cyber incident | Incident response / DFIR |
| Cloud risk | Cloud security |
| IT and cybersecurity together | Integrated IT and cybersecurity provider |
A small business experiencing repeated Microsoft 365 compromises, for example, may need MFA, administrator protection, email security, endpoint protection and sign-in monitoring before it needs an enterprise managed SOC.
A large industrial or critical-infrastructure organization may require much deeper specialist capability.
How to Choose a Cybersecurity Company in Saudi Arabia
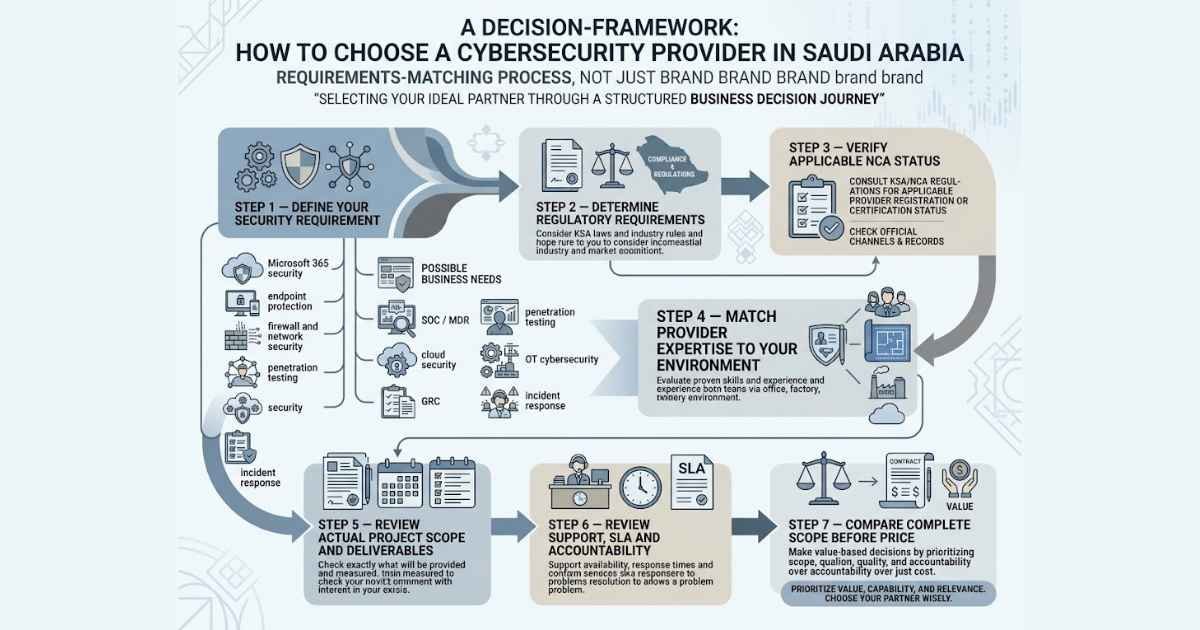
1. Define the Security Requirement
Start with the environment rather than a product package.
Understand:
- Critical systems
- Sensitive information
- Microsoft 365 and cloud usage
- Remote-access requirements
- Vendor access
- Network architecture
- OT/industrial systems
- Existing security controls
- Regulatory requirements
2. Verify Applicable NCA Status
Where required, check the provider against current NCA registration and licensing information.
If you are buying MSOC services, confirm the correct Tier 1 or Tier 2 licence directly with NCA.
Do not rely only on a logo on a provider’s website or an old blog article.
3. Match Expertise to Your Environment
An industrial company may prioritize OT security, segmentation, SCADA environments and vendor remote access.
An SME may instead need Microsoft 365 protection, endpoint security, firewall improvements, backups and day-to-day technical support.
Neither requirement is inherently more important—they require different expertise.
4. Ask What Will Actually Be Delivered
Avoid choosing a provider because of broad phrases such as “advanced security” or “complete cybersecurity.”
Ask:
- Which systems will be assessed?
- What tools or platforms will be used?
- What monitoring is included?
- What deliverables will be provided?
- Who investigates incidents?
- Is remediation included?
- Is retesting included?
5. Ask Who Will Perform the Work
Understand whether services will be delivered by:
- The provider’s Saudi team
- A subcontractor
- An overseas team
- A technology vendor
- A combination of teams
What matters is knowing who receives access to your environment and who remains accountable.
6. Review Support and Response
Clarify:
- Support hours
- Incident escalation
- SLA
- Emergency contacts
- On-site availability
- Data and log handling
- Subcontractors
- Contract-exit procedures
7. Compare Scope, Not Price Alone
A vulnerability scan, penetration test, full assessment, managed SOC and Microsoft 365 security project are very different services.
Compare what is actually included rather than the headline SAR amount.
Questions to Ask Before Hiring a Cybersecurity Provider
- Is your current NCA registration or licensing appropriate for the service we are purchasing?
- Does our service require MSOC licensing?
- Which services will your own team deliver?
- Will anything be subcontracted?
- Who will have privileged access?
- Where will security logs and customer data be processed?
- What relevant industry experience do you have?
- What assessments are included?
- Does the scope include remediation?
- Is retesting included?
- What incident-response SLA applies?
- How are serious alerts escalated?
- What documentation will we receive?
- What happens to accounts, data and access when the contract ends?
- For penetration testing, how are authorization, testing windows, exclusions and rules of engagement documented?
These questions are usually more useful than asking a provider simply to send its cybersecurity brochure.
Where Does NABCO Fit in a Saudi Cybersecurity Shortlist?
NABCO is most relevant where cybersecurity is closely linked with broader IT operations.
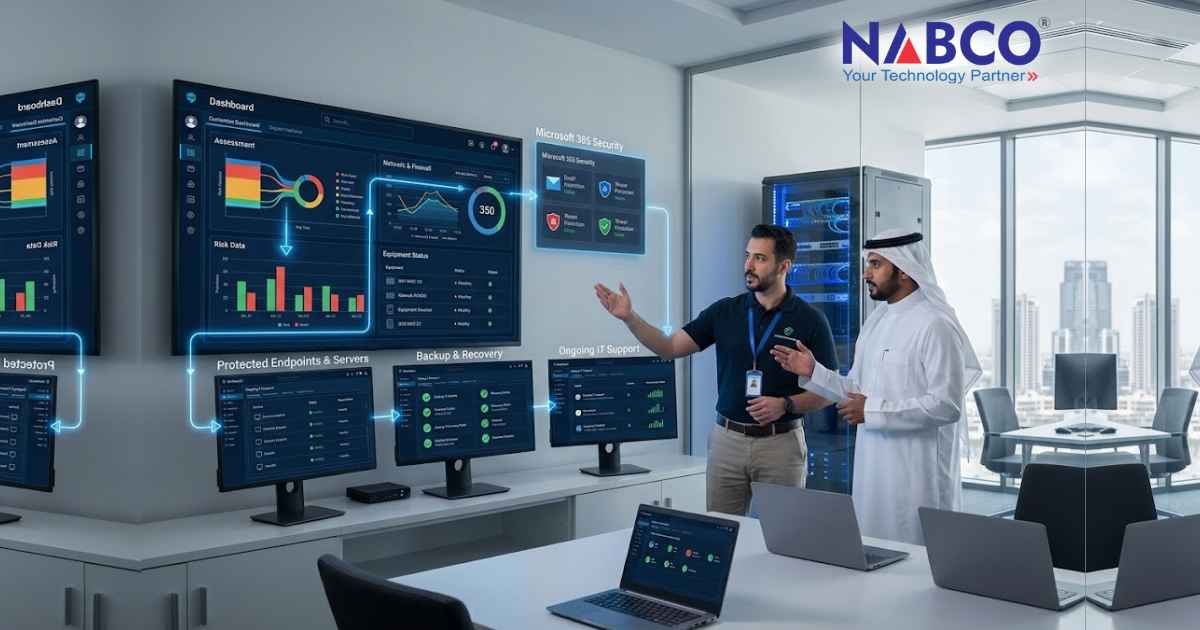
Its dedicated cybersecurity service page covers security across networks, endpoints, identities, cloud environments, Microsoft 365, email, vulnerability assessment and incident response. NABCO Cybersecurity Services
At the same time, its broader technology portfolio includes Microsoft/cloud, networking, servers, backup and managed IT services. NABCO Services
That combination can make NABCO particularly relevant for businesses that need to move from identifying a cybersecurity problem to actually improving the underlying environment.
For example:
Assessment → Firewall / Network → Microsoft 365 → Endpoint → Backup → Ongoing Support
rather than treating every problem as a separate standalone project.
Organizations needing national-scale MSOC capability, advanced specialist DFIR, highly specialized offensive security or dedicated OT cybersecurity engineering should evaluate providers with verified expertise and appropriate licensing for those requirements.
That is a more credible position than claiming that NABCO—or any provider—is universally “number one.”
Explore NABCO Cybersecurity Services
For NABCO’s complete current cybersecurity service portfolio:
Cybersecurity Solutions in Saudi Arabia — NABCO
Cybersecurity Provider Checklist for Saudi Businesses
Before making a final selection:
- ☐ Define the security problem
- ☐ Identify critical systems and data
- ☐ Determine regulatory requirements
- ☐ Verify applicable NCA status
- ☐ Verify MSOC licensing if relevant
- ☐ Review industry experience
- ☐ Review technical capability
- ☐ Understand who performs the work
- ☐ Identify subcontractors
- ☐ Review privileged-access procedures
- ☐ Check log/data handling
- ☐ Review SLA and escalation
- ☐ Confirm remediation scope
- ☐ Confirm retesting
- ☐ Review deliverables
- ☐ Understand contract-exit procedures
- ☐ Compare providers based on complete scope
Frequently Asked Questions
What are some leading cybersecurity companies in Saudi Arabia?
Selected providers include SITE, sirar by stc, Cyberani, SAMI-AEC, Innovative Solutions, Security Matterz, Sahara Net, Saudi Business Machines and NABCO.
They serve different market requirements, so inclusion should not be interpreted as a best-to-worst ranking.
Is NABCO a cybersecurity service provider in Saudi Arabia?
Yes. NABCO publicly offers a dedicated cybersecurity portfolio in Saudi Arabia covering network security, endpoint protection, identity and access management, vulnerability assessment and penetration testing, cloud and Microsoft 365 security, email security, incident response and related services.
View NABCO Cybersecurity Solutions
This service-provider positioning should be considered separately from NCA registration or MSOC Tier 1/Tier 2 licensing status.
Which cybersecurity company is best in Saudi Arabia?
There is no single best provider for every organization.
The right choice depends on business size, technology environment, industry, regulatory requirements and whether you need assessment, implementation, continuous monitoring or specialist security expertise.
What is the difference between NCA registration and MSOC licensing?
Provider registration applies to entities providing cybersecurity services, solutions or products as defined by NCA.
MSOC licensing specifically governs Managed Security Operations Center services.
Tier 1 and Tier 2 are therefore not general ratings of cybersecurity companies. National Cybersecurity Authority
What cybersecurity services should an SME consider?
Common priorities may include:
- Cybersecurity assessment
- MFA
- Microsoft 365 security
- Endpoint protection
- Firewall and network security
- Email security
- Backup and recovery
- Vulnerability management
- Employee awareness
An SME may benefit from an integrated IT and cybersecurity provider if several of these requirements need to be implemented together.
Should I choose a cybersecurity specialist or an IT-and-cybersecurity provider?
It depends on the problem.
Advanced MSOC, DFIR, specialist penetration testing or OT/ICS requirements may call for a specialist cybersecurity company.
A business that primarily needs secure Microsoft 365, networks, endpoints, firewall, backup, servers and ongoing IT support may benefit from a provider that integrates cybersecurity with broader IT infrastructure.
Final Thoughts
Choosing among cybersecurity companies in Saudi Arabia should not be treated as a popularity contest.
SITE, sirar by stc, Cyberani, SAMI-AEC and other licensed MSOC providers serve important enterprise and regulated-market requirements. Specialist firms offer additional managed, consulting, offensive-security and assurance capabilities.
NABCO also genuinely belongs in the Saudi cybersecurity-provider landscape, particularly for SMEs and mid-market businesses that need cybersecurity improvements integrated with networks, Microsoft 365, cloud, endpoints, servers, backup and ongoing IT infrastructure.
The correct comparison is therefore not simply:
“Which company is biggest?”
It is:
“Which provider has the right capabilities, regulatory standing, delivery model and support for our specific security problem?”
Define your requirements first, verify applicable NCA status, compare actual project scope and choose the provider that best fits your organization’s environment and risk.